
Compliance
Where do we stand?
All 110 requirements grouped by family, each with a status, an owner, the date it was last validated, and how many files back it up. The header counts the requirements holding zero evidence.
NIST SP 800-171 Rev 2
Overwatch 7Six keeps every file mapped to the requirement it supports, assigned to an owner, and stamped with the date it was last validated. All 110 requirements. All 14 families. One record you can stand behind.
Fifteen minutes against all 110 requirements. No account, and we never receive the result unless you send it to yourself.
Vigilant. Autonomous. Mission Ready.
The problem
Regulatory update · July 13, 2026
The Department of War suspended CMMC Phase II, the third-party assessment requirement (C3PAO at Level 2, DIBCAC at Level 3) that was due to take effect November 10, 2026. A CMMC Reform Task Force was given 60 days to deliver recommendations. That period closed in September 2026, and no change to contractual obligations has been published. Phase I self-assessment, NIST SP 800-171 Rev 2 reporting, SPRS scores, annual affirmations, and DFARS 252.204-7012 are unchanged. Self-assessed evidence still has to hold up.
Source · U.S. Department of War release, July 13, 2026 · Reviewed September 17, 2026
110 / 14
NIST SP 800-171 Rev 2 requirements, across 14 families. CMMC Level 2 requirements are identical to them
Source · 32 CFR § 170.14(c)(2); NIST SP 800-171 Rev 2
-203 to 110
SPRS score range. Each unmet requirement deducts 1, 3, or 5 points, with partial credit only where the methodology names it
Source · NIST SP 800-171 DoD Assessment Methodology v1.2.1, June 24, 2020
180 days
To close out every POA&M item after a Conditional CMMC Status, confirmed by a closeout assessment. Miss it and the Conditional status expires
Source · 32 CFR § 170.21
$52M / 9
Recovered in cybersecurity False Claims Act settlements in FY2025, across nine cases
Source · Outside-counsel analysis of DOJ FY2025 FCA statistics. DOJ's own release does not break out the cybersecurity figure
They don't know what systems are in scope for CUI.
Evidence is scattered across email, SharePoint, tickets, screenshots, cloud portals, and MSP reports.
Their MSP says “we handle security,” but nobody can prove which controls are covered.
Their SSP is incomplete, stale, or written in consultant language nobody owns.
POA&M items exist informally, with no clear owner or deadline attached.
Executives don't know what readiness means in contract-risk terms.
Technical teams don't know what evidence an assessor will expect to see.
SPRS scoring feels disconnected from the day-to-day remediation work.
Satisfying a NIST SP 800-171 control takes evidence: a config export, a ticket, a policy document, a log, mapped to the specific control and assessment objective it supports, with an owner and a validation date attached. Most defense contractors can point to their tools. Fewer can produce that evidence on request, in the format an assessor needs.
Each one answers a question you will be asked about your self-assessment.
Where do we stand?
All 110 requirements grouped by family, each with a status, an owner, the date it was last validated, and how many files back it up. The header counts the requirements holding zero evidence.

What is due?
The annual affirmation due date sits first. Open POA&M items sort by target date, and anything inside 30 days is marked. A planned assessment appears only once one is scheduled.

What is missing?
An assistant that reads your evidence metadata against NIST SP 800-171A assessment objectives and cites the objective identifier behind every observation. It reports what exists and what does not.
Attach a file to the requirement it speaks to. Confirm it holds no CUI. The file lands in storage scoped to your organization and nowhere else.
Every file carries the requirement it supports, who uploaded it, and when. Plain-language intent sits next to each requirement so the mapping is deliberate.
Log a validation and the record stamps the date and the person. Six months later you can still answer who checked this, and when.
Open POA&M items sort by target date. The affirmation card carries the next due date. Nothing depends on a calendar reminder someone forgot to set.
What this is
Overwatch 7Six doesn’t promise certification. The strongest language here is readiness, evidence, defensibility, assessment preparation, control implementation, and accountability.
Overwatch 7Six is
Overwatch 7Six is not
The federal lifecycle
01 · Scope
Identify which systems and data touch FCI or CUI. That determines the required CMMC level.
32 CFR § 170.19
02 · Assess
Self-assessment for Level 1 or Level 2 (Self), or a C3PAO or DIBCAC assessment for Level 2 (C3PAO) and Level 3.
32 CFR §§ 170.15–170.18
03 · Score
SPRS score submitted. A Level 2 POA&M item cannot exceed 1 point, with one named exception at 3 points for non-FIPS-validated CUI encryption.
DFARS 252.204-7019/7020; 32 CFR § 170.21(b)
04 · Conditional
180 days to close out the POA&M, confirmed by a closeout assessment. Miss it and the Conditional CMMC Status expires.
32 CFR § 170.21
05 · Final
Certified status. Valid for 3 years for a C3PAO or DIBCAC assessment.
32 CFR §§ 170.16–170.17
06 · Affirm
An affirming official reaffirms continuous compliance in SPRS every year the status stays current.
32 CFR § 170.22
AI doctrine
AI reduces friction. It doesn’t get to create unsupported claims on your behalf.
The assistant reads your evidence index, never your evidence. File names, the requirement each maps to, statuses, and validation dates reach the model. The contents of an uploaded file are never read and never sent.
Good AI uses
Bad AI uses
“Handoff rule: AI can assist, but every assessment-facing claim must trace back to evidence the customer can defend.”
Scope boundary
Overwatch 7Six holds evidence about your controls, not the regulated data itself. Screenshots of a policy setting, a signed training roster, an asset inventory. Every upload carries a required acknowledgment, and the database refuses any evidence row that does not have it. The checkbox is not the only gate.
“I confirm this file contains no Controlled Unclassified Information (CUI). Overwatch 7Sixdoes not accept CUI.”
The full catalog ships seeded. You start from the standard, not from an empty table.
22 requirements
3 requirements
9 requirements
9 requirements
11 requirements
3 requirements
6 requirements
9 requirements
2 requirements
6 requirements
3 requirements
4 requirements
16 requirements
7 requirements
What’s at stake
01
DOJ's Civil Cyber-Fraud Initiative, running since October 2021, has settled fifteen cybersecurity-related False Claims Act cases. Nine of them closed in fiscal year 2025 alone, recovering more than $52 million out of a record $6.8 billion in total FCA recoveries.
Outside-counsel analysis of DOJ FY2025 FCA statistics. The cybersecurity breakout is not in DOJ's own release
02
Georgia Tech Research Corporation and the Georgia Institute of Technology paid $875,000 on September 30, 2025. DOJ alleged no system security plan existed for the lab doing Air Force and DARPA work until at least February 2020, and that the assessment score of 98 submitted to DoD was false. Raytheon, its parent RTX, and successor Nightwing paid $8.4 million on May 1, 2025 over 29 contracts and subcontracts.
DOJ press releases, May 1 and September 30, 2025
03
DOJ's own framing of these cases: they are not about being breached. They are about certifying something to the government that wasn't true. An inaccurate SPRS score creates the exposure, whether or not an incident ever happens.
31 U.S.C. §§ 3729–3733; DOJ Civil Cyber-Fraud Initiative, announced October 2021
Five of the eight Initiative settlements DOJ announced during calendar year 2025 began as qui tam suits filed by insiders. The relators in the Georgia Tech case took $201,250. The former Raytheon director of engineering who filed that case took $1,512,000. A gap between what your SSP claims and what your evidence actually shows is a liability an employee can act on, not just an assessor.
Source · Outside-counsel analysis of DOJ settlement announcements. DOJ publishes no qui tam breakout for the Initiative
Product north star
“Show me why you believe this control is implemented.”
Whoever asks, a CEO, an IT manager, an MSP, or an assessor, Overwatch 7Six should make the answer easy to find, easy to explain, and hard to fake.
The founder
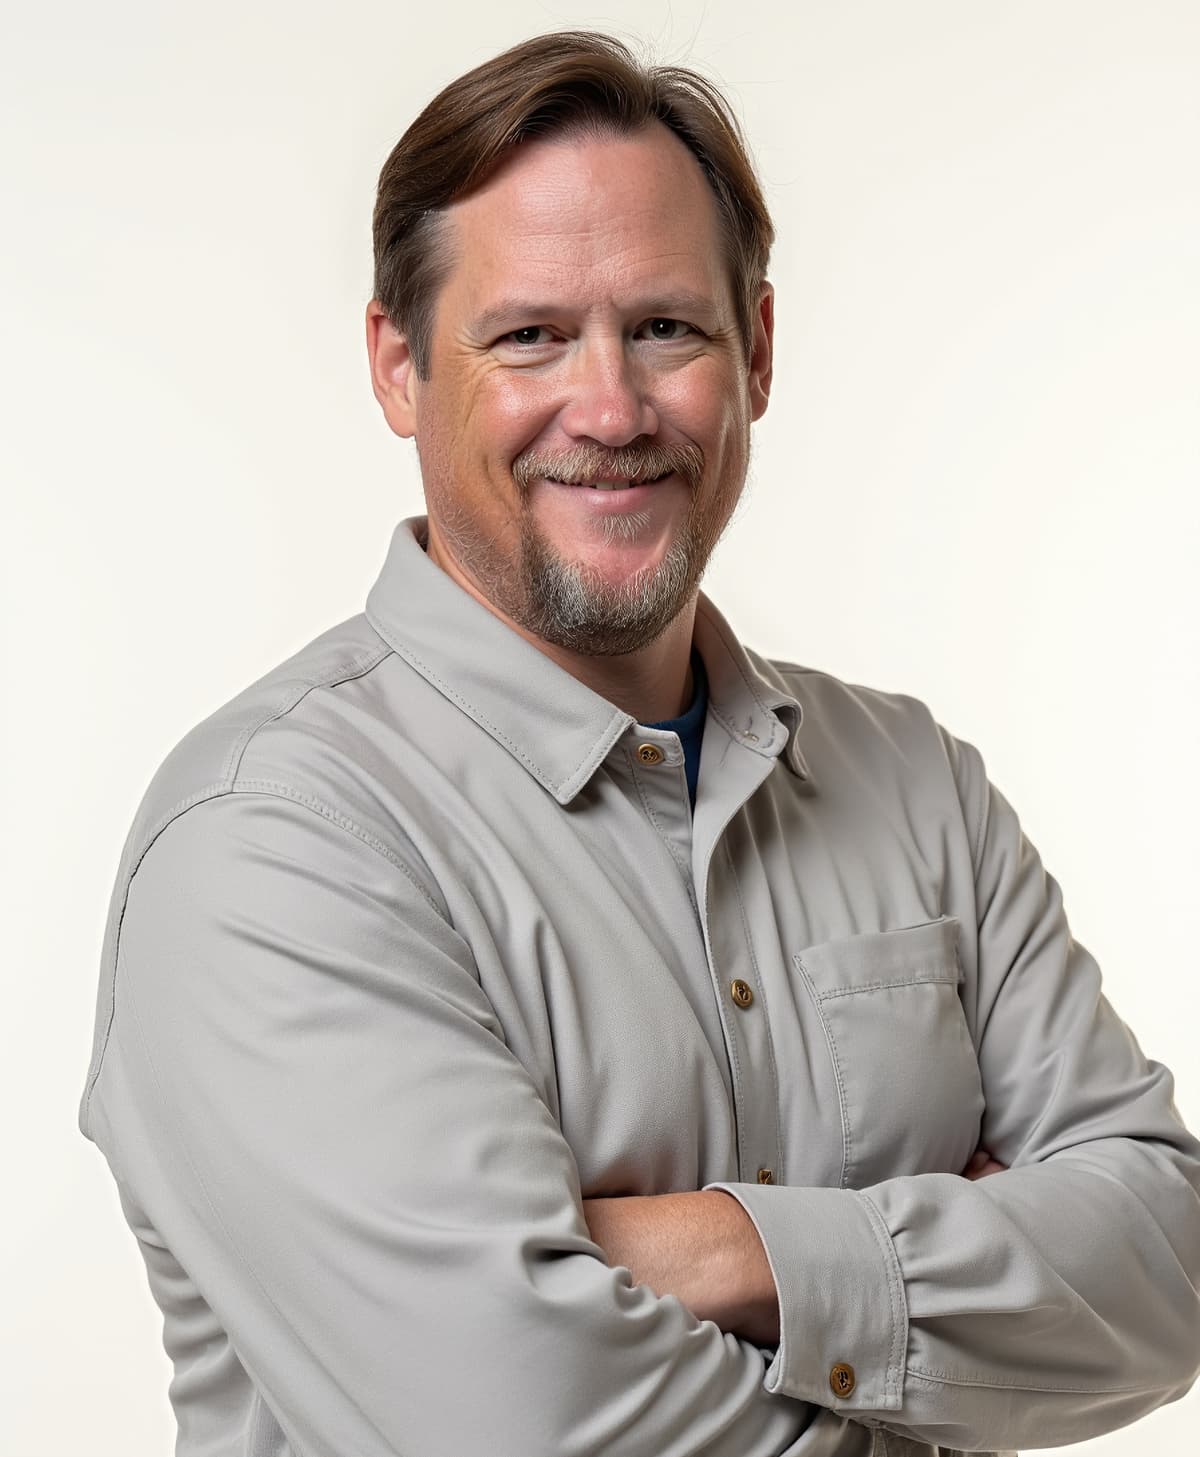
Texas Veterans Commission verified veteran-owned business
Bradley A. Baker
Founder & Sole Principal, Patriot 7Six LLC
Overwatch 7Six comes out of direct experience administering the M365 tenant and Mimecast for a clinical research organization under constant regulatory audit, where access control, retention, and evidence trails were the daily work. That work showed what happens when evidence lives in someone’s inbox instead of a system built to defend it in front of an assessor. For a defense contractor, that gap is the difference between a Final CMMC status and a Conditional one that runs out the clock.
Service record
Civilian record
Airborne-qualified infantryman with the 82nd Airborne Division, 1996–1999, earning the Expert Infantryman’s Badge. Promoted to Sergeant with the 172nd Infantry Brigade, Fort Wainwright, Alaska, 1999–2002. Two decades in enterprise IT since 2005, including SOX and FERPA-regulated environments, before founding Patriot 7Six LLC.
Stage & posture
Capital
Bootstrapped
Solo founder, building full-time on personal capital and earned time since leaving enterprise IT in September 2026. No outside dilution to date.
Build state
Overwatch 7Six · MVP build
In active development. Not yet live. This site describes the product being built, not a shipped platform.
Posture
Selectively open
Not actively raising. Open to mission-aligned angels, veteran-network professionals, and strategic partners: VSOs, PTACs, and government contracting consultants.
Data handling
Built on cloud-native infrastructure with encryption in transit and at rest, strict tenant isolation, and role-based access control. No customer PII, CUI, or unverified regulatory claim leaves the platform for a third-party tool without the customer’s knowledge.

Create an account and the 110-requirement catalog is waiting, scoped to your organization alone.
Create account